Inside the Mind of the Woman Who Built Britain’s Cybercrime Defence
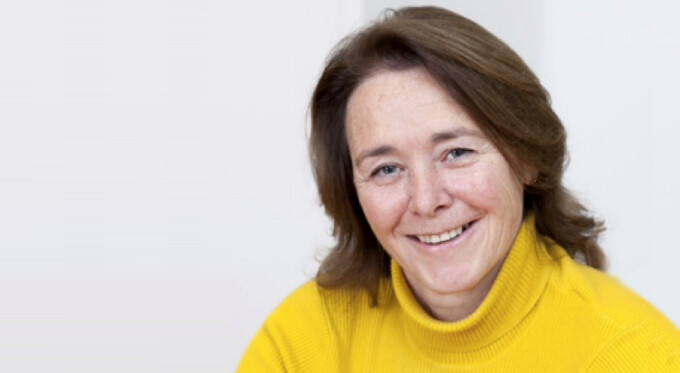
Charlie McMurdie is one of the UK’s most distinguished experts in cyber resilience, with a career that spans more than three decades in law enforcement and national security.
As the former Head of the Police National Cyber Crime Unit at Metropolitan Police Service and a senior advisor to leading global firms, she has been instrumental in building the country’s cyber-crime capabilities and shaping how organisations confront digital threats.
Her work stretches from covert operations in serious organised crime to establishing national forensic centres and advising on high-profile events such as the London 2012 Olympics. Today, she shares her insights as a sought-after cyber security speaker, equipping businesses and leaders with strategic advice on protecting their critical data and infrastructure.
In this exclusive interview with The Cyber Security Speakers Agency, Charlie opens up about the evolution of cyber-threats—from early denial-of-service attacks to the era of sophisticated ransomware—and outlines what organisations must do to adapt and thrive in an ever-more connected world.
Q: During your time in law enforcement, what forms of cybercrime were most prevalent — and how did organisations typically respond to them?
Charlie McMurdie: “I suppose at the time, so my former role — 32 years in law enforcement — and at that time, way back when into the late 1990s, I was running a number of serious and organised crime departments at Scotland Yard, one of which was the Fraud Squad. So, several hundred guys dealing with very long, protracted frauds — not my normal cup of tea, which was far more proactive, fast-paced criminal investigation type stuff.
“But because of the Fraud Squad work, I was doing lots with the banks. We started to see how the banks were having issues with fast-time money movement going through, mainly money laundering.
“When we were approaching companies to find out about some of the losses and some of the compromised data that was being used for transferring money, back then cyber wasn’t even a word — it was high-tech crime, it was digital crime, it was fraud, it was all traditional crime.
“Nobody wanted to talk about the fact that their organisation had been attacked or breached and data had been stolen, and their customers were losing money. It was all very under the table, kept quiet. We didn’t have any picture as to how much of this stuff was going on.
“Back to your question about what was the most prevalent type of stuff that was going on — we saw some attacks taking place, and I always say it was quite fortunate at the time, on the back of, you may recall, the Julian Assange WikiLeaks and the freedom of speech domain groups, primarily Anonymous, that started to launch attacks on organisations under the idea of having a right for their voice to be heard.
“That’s fine, but knocking over organisations dealing with money movement, such as PayPal or Mastercard, putting them out of service, caused significant harm. So, we saw early-day attacks — only because other stuff wasn’t being reported so much — a lot of denial-of-service attacks knocking over organisations.
“You may recall groups like Fathers for Justice jumped on the bandwagon and were attacking organisations. So, the most prominent, visible type of cybercrime we saw was a lot of denial-of-service attacks bashing organisations over.”
Q: Ransomware has become one of the biggest threats facing businesses today. From your experience, why is it so damaging, and how can organisations prepare for it?
Charlie McMurdie: “Again, and how it’s developed and become far more sophisticated and that really causes significant harm to businesses — certainly when organisations are hit with this type of attack, it can be the rabbit in the headlights, like, “What do we do now?” Ransomware.
“I remember way back in the day when ransomware was quite straightforward — you’d receive an email, and your computer would be locked down because you’d been doing illegal file sharing or downloading music that you weren’t allowed to download. You’d get this symbol or sign come up on your screen saying you have been fined 50 Euros or 50 pounds and to pay your money now.
“I really remember early days when they were actually using our police logo — we’d set up our original cybercrime unit in law enforcement, the Police Central e-Crime Unit, and they were using our logo as one of the warnings saying, “You’ve been locked down for file sharing, you need to pay the PECU money.”
“We thought that might help with our funding challenges at the time, but that was very low-level. Nowadays, you see companies and big organisations — most recently we’ve seen the NHS, the health sector, government sector — anywhere where there’s really rich data, and they know that they can cause significant harm. They like the legal sector, the health sector, financial sector. It’s not a straightforward attack and lock that organisation down now.”
Q: With new technologies constantly emerging, how can cybersecurity teams evolve fast enough to keep pace with digital criminals?
Charlie McMurdie: “Everything is now being connected to our networks, and every day there is some development around technology and new bits of kit for both defending and lots of kit being developed by the attackers. So, how do we actually stay match-fit to deal with cyberattacks and the cyber technology that’s out there? I think key to all of that is really getting the right people in place.
“A lot of my old cyber unit were detectives from Flying Squad; we had loads of industry players, and it’s that mindset — people who are keen to stay match-fit, keep up the pace, keep up the learning, keep the interest and the development going — because technology changes at such a pace that if you’re good at doing a certain aspect and dealing with a certain technology today, you’ll fall behind. You have to have that intrigue, that interested mind.
“The other thing is that nobody can deal with cyber in isolation. It’s a team game. You look at the attackers — they’ll have their own organised networks, their own criminal networks, and they’ll headhunt individuals to form part of their attack network from around the world.
“They’re almost checking their CVs and hiring. We need to mirror that. We need to be sharing intelligence, working with the best people, and having networks of sharing intelligence as to what’s going on and what’s happening.”
Q: The rise of remote working has changed how organisations operate. How have cybercriminals adapted their tactics in response?
Charlie McMurdie: “We saw, with COVID causing all the problems, that it was a big nudge — a big push — towards lots more people using their own bits of kit, their own laptops, their own phones, lots more working from home.
“Own devices being used, and we saw a massive increase in attacks and harvesting data, and certainly cybercrime on the back of people pretending to be government bodies offering furlough payments or COVID support — “You need to click on this, that, and the other.”
“Any hot topic, the criminals will utilise that for their advantage. Now, people are working far more remotely, and obviously that opens up more doors for the cybercriminals. But I think we shouldn’t steer away from that. I think working from home, as long as it’s done following the right processes and procedures that businesses put in place, should be a great enabler.
“Where we can fall short is when people don’t follow the right process, haven’t got the right security, AV, or aren’t using the right company procedures. To put a simple example in place, we’ve seen some breaches where, once they actually breach, you think, “Why are they stealing data from that company?”
“There’s no financial gain to be had, no real incentive — but when you look at the people who may have their data within that company database, for example, Charlie McMurdie in that database that’s just been harvested, whether it’s a social media database or selling toilet rolls, something particularly insignificant — if Charlie McMurdie uses the same password on that database as she uses on her company email, then that becomes a problem.
“We’ve seen that can be used as a very simplistic tool because people use the same password on many different platforms and forums. So that gives a leg up to the attackers.”
This exclusive interview with Charlie McMurdie was conducted by The Motivational Speakers Agency.




