SPF Check and Lookup Guide: Verify Your DNS SPF Record and Fix Common Errors

SPF Fundamentals: What Sender Policy Framework Is and Why It Matters
Sender Policy Framework (SPF) is an email authentication standard defined in RFC7208. It lets a domain publish a policy, via DNS, listing authorized senders and authorized IP addresses that can send mail on its behalf. Receiving systems compare the connecting IP address during SMTP (Simple Mail Transfer Protocol) with that DNS SPF record to decide whether to accept, quarantine, or reject emails. By verifying a sender IP against a published SPF record, organizations reduce email spoofing, phishing, and spam, improving overall email security and email deliverability.
How SPF Works in the SMTP Flow
- A sending mail server connects to the recipient’s mail server using the Simple Mail Transfer Protocol.
- The recipient extracts the envelope-from (Return-Path) domain and the sender IP address.
- The recipient performs an SPF check by looking up the DNS TXT record (the DNS SPF record) for that domain.
- The SPF policy result (pass, fail, softfail, neutral, temperror, permerror) informs the spam filter to accept, flag, or reject emails. This email validation step helps prevent bounced messages and reduces the risk of email bounce due to spoofing.
SPF, DKIM, and DMARC Together
SPF is one pillar of email authentication. DKIM uses cryptographic signatures, and DMARC aligns SPF and/or DKIM with the visible From: email domain to specify how to handle failures (monitor, quarantine, or reject). Together, SPF + DKIM + DMARC provide layered email spoofing prevention and compliance controls.
Locate and Read Your SPF Record: DNS TXT Basics, v=spf1 Syntax, Mechanisms, Qualifiers, and Modifiers
An SPF policy lives in a TXT record at the root of an email domain (or a subdomain used for delegated email). You’ll identify it by the prefix v=spf1. This DNS SPF record enumerates a list of authorized servers via mechanisms and can reference other domains via the include tag or redirect tag.
DNS TXT Basics and Related Records
- DNS TXT record: Where the SPF record is published (often alongside other TXT data).
- DNS A Record / DNS AAAA Record: Used by the a mechanism to authorize the IPs that resolve from a host.
- DNS MX Record: Used by the mx mechanism to authorize IPs of your mail exchangers.
- DNS CNAME Record: Not valid for the AutoSPF record itself; publish SPF as a TXT, not CNAME.
- DNS PTR Record: The ptr mechanism is deprecated for SPF due to reliability concerns.
- DNS NS Record, DNS SOA Record, DNS SRV Record, DNSKEY, DS Records: Other Domain Name System records you may manage (DNSKEY/DS support DNSSEC for integrity). In cloud-based DNS platforms like Cloudflare or Cloudflare Registrar, you’ll manage all these DNS record types centrally.
Readable SPF Record Example
A simple SPF record example for examplesender.net: v=spf1 ip4:203.0.113.10 ip6:2001:db8::10 include:_spf.examplesender.email -all
- v=spf1 denotes the version.
- ip4/ip6 mechanisms list authorized IP addresses directly.
- include:_spf.examplesender.email references an included domain that publishes a list of authorized servers.
- -all is a hard fail, signaling receivers to reject emails not matching the mechanisms.
Key Components Annotated
- Mechanisms: ip4, ip6, a, mx, exists, include, all.
- Qualifiers: + (pass, default), – (fail), ~ (softfail), ? (neutral).
- Modifiers: redirect= (redirect tag to another policy), exp= (explanatory text; rarely used in practice).
- Components of SPF record: v=spf1 prefix, mechanisms for authorized senders, qualifiers for disposition, and optional modifiers.
Why ptr Is Deprecated
Although the SPF specification once allowed ptr, modern guidance deprecates it. Depending on reverse DNS (DNS PTR Record) is slow and error-prone. Replace ptr with explicit ip4/ip6 or a/mx mechanisms to keep lookups predictable and your DNS SPF record robust.
Perform an SPF Check/Lookup: CLI Commands, Online Validators, and a Step-by-Step Verification Workflow
You can check SPF record content and results with command-line tools or online validators. Always expand includes to verify the full list of authorized senders.
CLI Commands
Use these to check SPF and the TXT record for your domain:
- Linux/macOS (dig): dig +short TXT examplesender.net
- Linux/macOS (host): host -t TXT examplesender.net
- Windows (nslookup): nslookup -type=TXT examplesender.net
Inspect MX and A Relationships
- dig +short MX examplesender.net
- dig +short A mail.examplesender.net; dig +short AAAA mail.examplesender.net These confirm how mx or a mechanisms translate to an IP address set.
Simulate a Sender IP
Many validators let you input a sender IP to test pass/fail against your DNS SPF record, mirroring an actual SMTP connect.
Online Validators and DNS Wizard Tools
- Cloud-based DNS providers like Cloudflare offer dashboards to view and edit your DNS record set, and educational resources on theNET and the Security Learning Center.
- An Email Security DNS Wizard can guide setting up SPF record syntax, DMARC, and DKIM in a single workflow.
- Reference materials from the Performance Learning Center and Access Management Learning Center can help with email validation and access design patterns.

Step-by-Step Verification Workflow
- Inventory sources: List every third-party email sender, in-house mail server, and delegated email subdomain.
- Locate the TXT record: Confirm a single v=spf1 line for your email domain.
- Expand includes: Resolve each include tag to ensure the included domain publishes valid authorized IP addresses.
- Count DNS lookups: SPF limits you to 10 DNS-mechanism lookups per evaluation.
- Test representative traffic: For each sender IP, perform an SPF check (pass/fail) and note any reject emails.
- Align policies: Confirm -all or ~all fits your risk posture and DMARC enforcement stage.
- Re-test after edits: Propagate changes in DNS and re-run your SPF check.
Fix Common SPF Errors: Multiple Records, 10-DNS-Lookup Limit, Bad Includes, ~all vs -all, Deprecated ptr, Syntax Issues
Small misconfigurations can turn into an invalid SPF record or weaken email authentication.
Multiple or Invalid Records
Symptoms: Two or more TXT records start with v=spf1. Receivers may treat the SPF record as invalid. Fix: Merge mechanisms into a single TXT record. Keep one authoritative DNS SPF record per domain or subdomain.
Hitting the 10-Lookup Limit and Safe Flattening
Symptoms: Too many include, a, mx, or exists lookups cause permerror; messages may be treated as spam. Fix:
- Consolidate senders and remove redundant mechanisms.
- Prefer ip4/ip6 where feasible.
- Use provider-maintained includes sparingly; consider safe flattening to replace volatile includes with a curated list of IP addresses. Automate refresh to track provider updates.
Bad Include or Redirect Tags
Symptoms: An include tag points to a zone with no SPF policy, or a redirect tag loops. Fix: Verify the included domain publishes v=spf1, and that redirect= points to a valid SPF record. Avoid chaining too many includes.
Choosing ~all vs -all
- ~all (softfail): Safer during rollout; messages might still pass through some filters but be marked.
- -all (fail): Strong stance to reject emails from non-authorized senders. Move to -all after monitoring DMARC reports to avoid unintended email bounce.
Syntax Issues and Deprecated Mechanisms
- Quote the TXT record correctly; avoid stray characters or line wraps.
- Do not use ptr. Keep mechanisms and qualifiers in supported formats.
- Remember that CNAME is not valid for the SPF record host.
Quick Remediation Checklist
- Single TXT record with v=spf1
- Mechanisms resolve to the intended list of authorized servers
- Total DNS lookups ≤ 10
- No ptr; clear final qualifier (~all during testing, -all for enforcement)
- Verified with CLI and at least one online SPF check tool
Ongoing Health and Best Practices: Testing Changes, Safe Flattening, Provider Updates, Monitoring, and Audits
Strong email authentication requires maintenance. Treat the DNS SPF record as living documentation of your sending ecosystem.
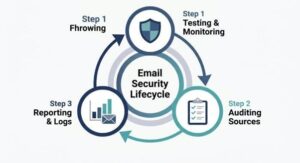
Change-Control Testing and Monitoring
- In staging, use ~all and DMARC p=none to collect data before enforcement.
- After edits, re-run an SPF check and observe spam filter behaviour and bounced messages for several days.
Auditing Sources and Provider Updates
- Keep an internal list of authorized senders and authorized IP addresses. Track every third-party email sender used by marketing, CRM, or billing.
- Review vendor notices; IP ranges shift. Version-control your SPF policy in an internal repository (for example, a “Redwood Blade Repository” or similar) for rollback safety.
Instrumentation and Reporting
- Enable DMARC aggregate (rua) and forensic (ruf) reports to see Return-Path alignment and failures.
- Log SMTP connection attempts on your mail server to spot unauthorized sources.
- For organizations using Cloudflare Registrar or similar, centralize DNS changes and document approvals for compliance.
When to Engage Experts
If you manage many domains or complex delegated email flows, involve your domain administrator or domain operator. Training from the Security Learning Center, Performance Learning Center, or Access Management Learning Center can accelerate team proficiency. Industry analyses (e.g., IDC MarketScape) and practitioner hubs like theNET provide context on evolving email security practices.




